Alternatives and Complements to Cyber Insurance
Cyber insurance is one tool among several that businesses can use to manage cyber risk.
Prevention Measures
Investing in cybersecurity measures—firewalls, antivirus software, multi-factor authentication, employee training, and regular software updates—can reduce both the likelihood of incidents and insurance premiums.
Incident Response Planning
Having a documented plan for responding to cyber incidents helps minimize damage and demonstrates to insurers that your business takes security seriously.
Risk Transfer Through Contracts
When working with vendors who handle your data, contractual provisions can shift some liability. However, this doesn’t eliminate your exposure entirely.
Self-Insurance
Some businesses may choose to set aside reserves to cover potential cyber losses rather than purchasing insurance. This approach may work for very small businesses with minimal exposure but becomes increasingly risky as digital dependency and data volumes grow.
Tips for Purchasing Cyber Insurance
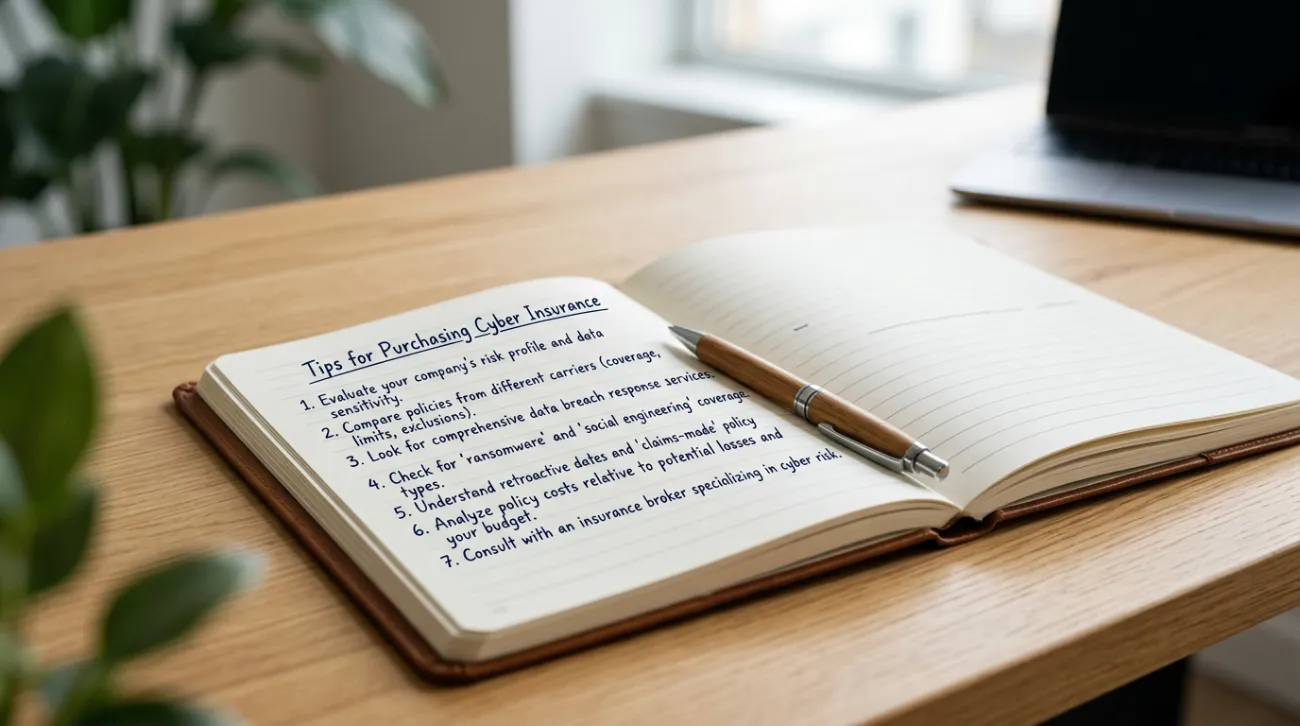
If you decide cyber insurance makes sense for your business, consider these approaches to getting appropriate coverage:
- Work with a knowledgeable broker: Cyber insurance is specialized. Brokers with experience in this area can help match your needs with appropriate policies.
- Compare multiple quotes: Coverage terms and pricing vary significantly between insurers. Getting several quotes helps ensure competitive pricing and appropriate coverage.
- Read the policy carefully: Pay particular attention to coverage triggers, exclusions, and conditions you must meet for coverage to apply.
- Be honest on applications: Misrepresenting your security practices can void coverage when you need it most.
- Consider policy limits carefully: Ensure coverage limits are adequate for realistic worst-case scenarios, including regulatory fines and business interruption.
- Review annually: As your business evolves, coverage needs change. Annual policy reviews ensure coverage remains appropriate.
The Bottom Line: Is Cyber Insurance Worth It?
For many small businesses, cyber insurance represents a prudent risk management investment. The potential costs of cyber incidents—particularly when accounting for business interruption, regulatory compliance, and liability exposure—often far exceed annual premium costs.
However, the value proposition depends heavily on individual circumstances. Businesses with minimal digital operations, no sensitive customer data, and strong financial reserves may reasonably conclude that cyber insurance isn’t essential. Conversely, businesses handling sensitive data, dependent on digital systems for revenue, or operating in regulated industries often find cyber insurance to be an important financial safeguard.
The decision ultimately comes down to an honest assessment of risk exposure, potential financial impact, and your business’s ability to absorb losses. For businesses where a significant cyber incident could threaten viability, the relatively modest cost of insurance premiums often proves worthwhile as a financial safety net—provided it’s combined with reasonable security practices rather than treated as a substitute for them.
Frequently Asked Questions
Typically, no. Traditional general liability and commercial property policies were not designed to address cyber risks and usually contain explicit exclusions for data breaches, cyber attacks, and related incidents. While some business owner’s policies (BOPs) now offer cyber endorsements, these often provide limited coverage compared to standalone cyber policies. Review your existing policies carefully and consult with your insurance agent to understand exactly what cyber-related coverage, if any, you currently have.
Timing varies based on the complexity of the incident and the specific insurer, but many cyber policies are designed to provide rapid response. For immediate expenses like forensic investigation and breach response, insurers often work with pre-approved vendors and may pay those vendors directly, speeding the process. More complex claims involving business interruption calculations or disputed liability may take longer to resolve. Working with your insurer’s designated incident response resources from the outset typically produces faster claim resolution.
Filing a claim may affect future premiums, similar to other types of insurance. Insurers consider claims history when pricing renewals. However, the impact varies by insurer and by the nature and severity of the incident. Some insurers may also consider whether you’ve implemented improved security measures following an incident. The potential for premium increases shouldn’t discourage legitimate claims—the coverage exists to be used when needed—but it’s a factor to be aware of.
Using cloud services doesn’t eliminate the need for cyber insurance. While reputable cloud providers implement strong security measures, your business remains responsible for how you access and use those services, for data you download or store locally, and potentially for breaches caused by compromised credentials. Additionally, cloud service agreements typically limit provider liability significantly, meaning losses from incidents affecting your cloud data may fall largely on your business.
Requirements vary by insurer and policy type, but common expectations include: using antivirus and anti-malware software, implementing firewalls, requiring multi-factor authentication for remote access and sensitive systems, regularly updating and patching software, maintaining data backups, and providing employee security awareness training. Some insurers require completion of detailed security questionnaires and may deny coverage or claims if stated security measures aren’t actually in place. Higher-risk industries or larger coverage amounts typically face more stringent requirements.
Ideally, both should proceed together. Having basic security measures in place helps you qualify for coverage and may reduce premiums. However, waiting until you have “perfect” security before purchasing insurance leaves you exposed during the improvement period. A practical approach is to implement fundamental security measures—multi-factor authentication, current antivirus, regular backups—then purchase insurance while continuing to strengthen your security posture. View insurance and security improvements as complementary, not sequential, investments.
Sources
- FBI Cyber Crime Division
- Cybersecurity and Infrastructure Security Agency (CISA) – Cybersecurity Best Practices
- National Association of Insurance Commissioners (NAIC) – Cyber Risk Resources
- U.S. Small Business Administration – Cybersecurity Guidance
- Federal Trade Commission – Data Security Guidance for Businesses